TL;DR
A DNS proxy sits between your device and a DNS server, forwarding domain lookup requests and caching the answers. It speeds up browsing, gives you control over which DNS servers handle which queries, and adds a filtering layer for security. It does not hide your IP address or route your actual traffic, so if anonymity is the goal, you need a full proxy instead.
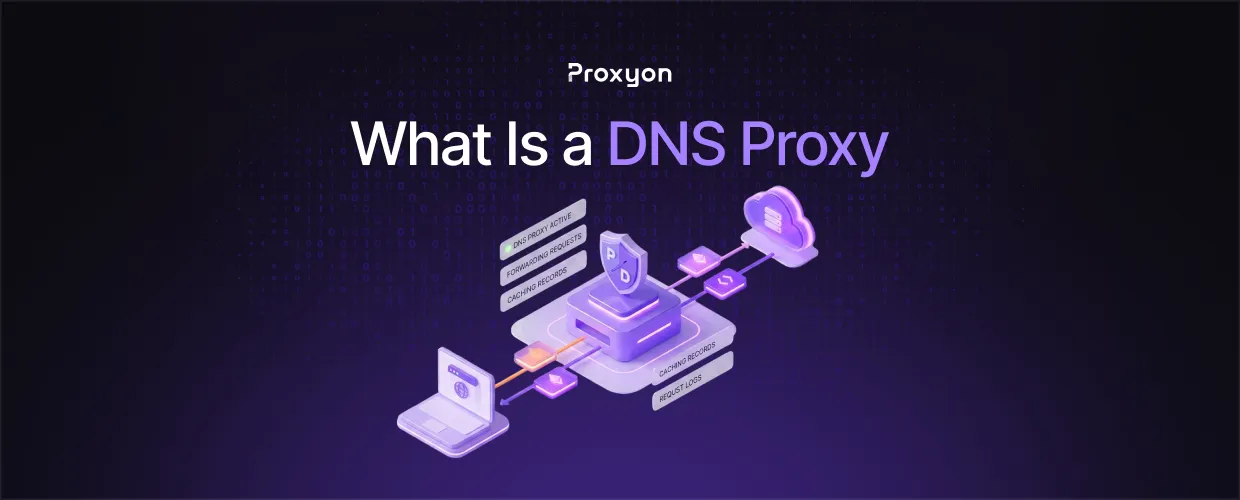
Every time you open a website, your device asks a DNS server to translate the domain name into an IP address. A DNS proxy is a server that sits in the middle of that exchange, receiving the lookup request, answering it from its own cache when possible, and forwarding it to an upstream DNS server when it is not. In this article, we'll explore how a DNS proxy works, what it is actually good for, how it differs from a regular proxy, and when you need something more.
How a DNS Proxy Works
The process is simple. Your device sends a DNS query to the proxy instead of directly to a resolver. The proxy checks its cache first. If the domain was resolved recently and the record has not expired, it returns the stored IP address instantly.
If the record is not cached, the proxy forwards the query to an upstream DNS server, sends the answer back to you, and stores it for next time. Each cached entry carries a TTL (time-to-live) value, and the proxy purges the record once that timer expires, as defined in the original DNS specification, RFC 1035. The result is faster lookups, since repeated queries skip the round trip to an external resolver entirely.
What a DNS Proxy Is Used For
Caching is the obvious benefit, but control matters just as much. A DNS proxy lets you decide which DNS servers answer which queries. Businesses use split DNS to send internal domain lookups to a corporate DNS server while everything else goes to a public resolver, which keeps internal hostnames from leaking to the ISP.
Filtering is the third use. Because every lookup passes through one point, the proxy can block queries to known malicious domains before a connection is ever made. Cloudflare's DNS overview explains how the resolution chain works and why intercepting it early is an effective security layer.
Some setups also use a DNS proxy to unblock region-locked streaming. The proxy answers location-check lookups with different values, which is how smart DNS services work under the hood.
Also Read: How to Use a Proxy for Video Streaming (2026)
DNS Proxy vs Regular Proxy
The keyword here is scope. A DNS proxy only handles domain lookups. Your actual traffic, the HTTP requests, the downloads, the page content, still travels directly from your real IP address to the destination. Nothing about your identity changes.
A regular proxy routes the traffic itself. Residential proxies replace your IP with one from a real household device, which is what you need for scraping, multi-account work, or anything where the target sees your address. Datacenter proxies do the same at higher speed and lower cost, with easier detectability as the trade-off.
This matters more than it sounds. A DNS proxy will not stop a website from blocking you, rate-limiting you, or logging your IP. If the site can see your real address, a DNS proxy changes nothing on their end.
Also Read: How to Use a Proxy Server on Any Device (2026)
The Limits Worth Knowing
A DNS proxy does not encrypt anything by default. Standard DNS queries travel in plaintext over UDP port 53, readable by anyone on the path. Encrypted variants like DNS-over-HTTPS and DNS-over-TLS fix this, but only if both the proxy and the upstream server support them.
It also does not prevent DNS leaks. If your device falls back to the ISP resolver, some queries bypass the proxy entirely, so verifying your configuration is part of the job.
FAQ Section
Does a DNS proxy hide my IP address?
No. It only changes which server answers your domain lookups. Your traffic still leaves from your real IP, and every website you visit can see it.
Is a DNS proxy the same as a smart DNS?
Close, but not identical. Smart DNS is a commercial service built on DNS proxying, tuned specifically to answer location checks with values that unblock streaming content.
Is a DNS proxy faster than a VPN?
Yes, because it does not encrypt or reroute your traffic. Only the small lookup packets pass through it, so your connection speed stays untouched.
Can I use a DNS proxy for web scraping?
Not on its own. Scraping targets block by IP address, and a DNS proxy does not change yours. You need rotating residential or datacenter proxies for that.
Does a DNS proxy encrypt my queries?
Not by default. Plain DNS is unencrypted. You need DNS-over-HTTPS or DNS-over-TLS support on both ends for encrypted lookups.
What is split DNS?
A configuration where the proxy routes queries to different DNS servers based on the domain. Internal company domains go to a private resolver, everything else goes to a public one.
Can a DNS proxy block malicious websites?
Yes. Since every lookup passes through it, the proxy can refuse to resolve domains on a blocklist, which stops the connection before it starts.
Final Thoughts
A DNS proxy is the right call when you want faster lookups, query control, or domain-level filtering. It is the wrong tool when you need to change your IP, because your traffic never touches it. For anything involving blocks, geo-restrictions, or scraping, a full proxy does what a DNS proxy cannot.