How VPN Passthrough Works With NAT
Your router uses NAT (Network Address Translation) to share one public IP across every device in your home. It tracks each connection by IP address and port number, then sends replies back to the right device. TCP and UDP traffic carry ports, so NAT handles them without any help.
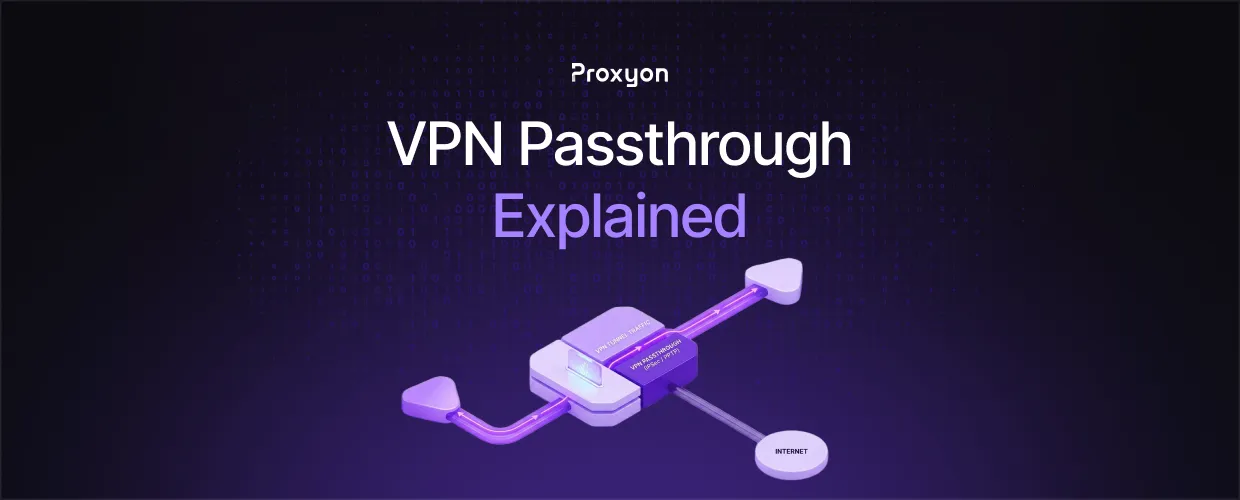
Some older VPN protocols carry no ports at all. Passthrough is a protocol-specific helper, often labeled ALG in router menus, that gives NAT another field to track the session by.
PPTP and GRE
PPTP opens a control connection on TCP port 1723, then sends the tunnel data over GRE, which has no ports. PPTP passthrough reads the Call ID inside the GRE header and uses it in place of a port number.
IPsec and ESP
Classic IPsec sends its data as ESP, which is encrypted and also portless. IPsec passthrough tracks those packets by their Security Parameter Index (SPI) instead, while the key exchange runs over UDP port 500.
L2TP
Plain L2TP is ordinary UDP on port 1701 and crosses NAT fine. In practice it almost always runs inside IPsec, so L2TP passthrough is really IPsec passthrough under a different label.
Also Read: Proxy vs VPN (2026)
VPN Passthrough Myths Worth Correcting
Several top-ranking guides say IPsec passthrough works by using NAT-T. It does not. NAT-T, defined in RFC 3948, is negotiated between the VPN client and the VPN server, which wrap ESP inside UDP port 4500. Once that happens, the router sees normal UDP and passthrough has nothing left to do.
Passthrough is also described as a way to bypass NAT or open ports. Neither is true. Your traffic still gets translated, and the helper only follows sessions started from inside your network. Unsolicited inbound traffic is still dropped, which is the job of port forwarding, a separate feature.
One more detail most guides skip: passthrough cannot rescue every kind of IPsec. The AH mode signs the IP addresses themselves, so any NAT rewrite breaks it. RFC 3715 calls NAT and AH fundamentally incompatible, which is why TP-Link's passthrough documentation lists IPsec support as ESP only.
Should You Enable VPN Passthrough in 2026
When to Keep It On
Keep IPsec passthrough on if anyone in your home or office connects to a company network with an older IPsec client. If two people on the same network cannot connect to the same office VPN at the same time, the router is likely refusing to rewrite UDP port 500, which limits it to one client per VPN server. Ask your IT team to enable NAT-T on their end.
When to Turn It Off
WireGuard runs over UDP, OpenVPN runs over UDP or TCP, and IKEv2 has NAT-T built in. If nobody uses PPTP, switch PPTP passthrough off, since the protocol has been considered broken for over a decade. You will usually find the toggles under Security, Firewall, or NAT settings, labeled ALG on TP-Link and NAT Passthrough on Asus.
Proxies Do Not Need Passthrough
HTTP and SOCKS5 proxies run over TCP, so NAT treats them like any other connection. A scraper routing through residential proxies or datacenter proxies behaves the same on any router, with or without passthrough enabled.
Also Read: How to Fix ERR_ADDRESS_UNREACHABLE (2026)
FAQ Section
Should VPN passthrough be on or off?
Leave IPsec passthrough on if anyone uses an older work VPN client. Turn PPTP passthrough off if nobody uses PPTP. Modern VPN apps work either way.
Does VPN passthrough slow down my internet?
No. It only helps the router track certain VPN sessions. Any slowdown comes from the VPN itself, not the passthrough setting.
Is VPN passthrough the same as port forwarding?
No. Port forwarding lets outside traffic reach a device inside your network. Passthrough only helps connections that your own devices start.
Is VPN passthrough the same as a VPN router?
No. A VPN router runs the VPN connection itself for every device behind it. Passthrough runs no VPN at all and only lets VPN traffic from your devices through.
Do WireGuard and OpenVPN need VPN passthrough?
No. Both use standard UDP or TCP, which NAT already handles. IKEv2 does not need it either because NAT-T is part of the protocol.
Is IP passthrough the same as VPN passthrough?
No. IP passthrough is an ISP gateway feature that hands your public IP to your own router to avoid double NAT. Turn it on only if you run your own router behind the ISP box.
Final Thoughts
VPN passthrough is a compatibility patch for PPTP and older IPsec clients, nothing more. It does not encrypt your traffic, open your network, or do anything for modern VPN protocols. Leave IPsec passthrough on if someone still relies on an old work VPN, and switch PPTP passthrough off if nobody does. If your real goal is routing traffic through different IPs for scraping or testing.